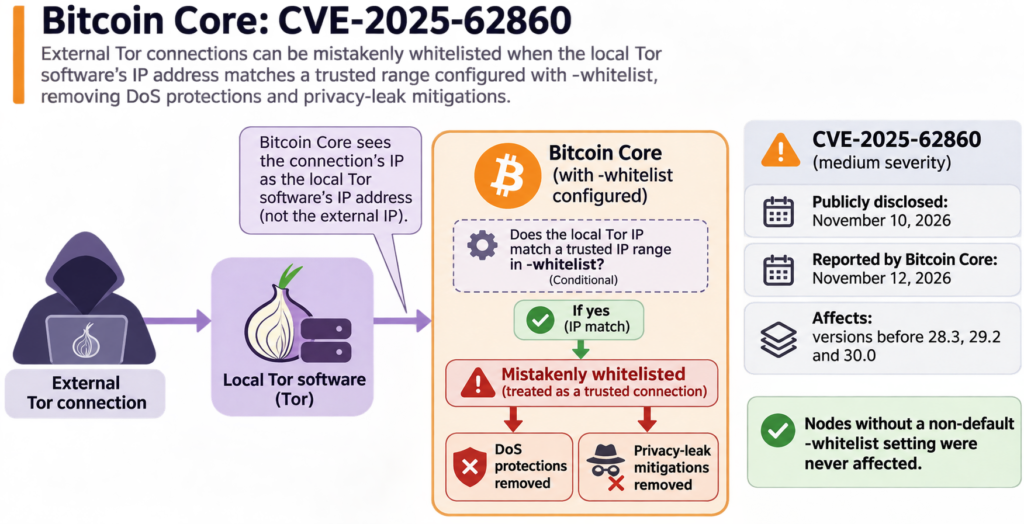
Operators using Bitcoin Core’s non-default -whitelist option should check whether it trusts the IP address of their local Tor software. In reporting dated November 12, 2026, Bitcoin Core identified a medium-severity vulnerability, CVE-2025-62860, that was publicly disclosed on November 10. It affects versions before 28.3, 29.2 and 30.0.
For an external connection arriving through Tor, Bitcoin Core sees the local Tor software’s IP address. If that address falls within a trusted IP range configured with -whitelist, Bitcoin Core can mistakenly whitelist the external connection. That removes denial-of-service (DoS) protections and privacy-leak mitigations that would otherwise apply to the connection.
The disclosure states that nodes without a non-default -whitelist setting were never affected.