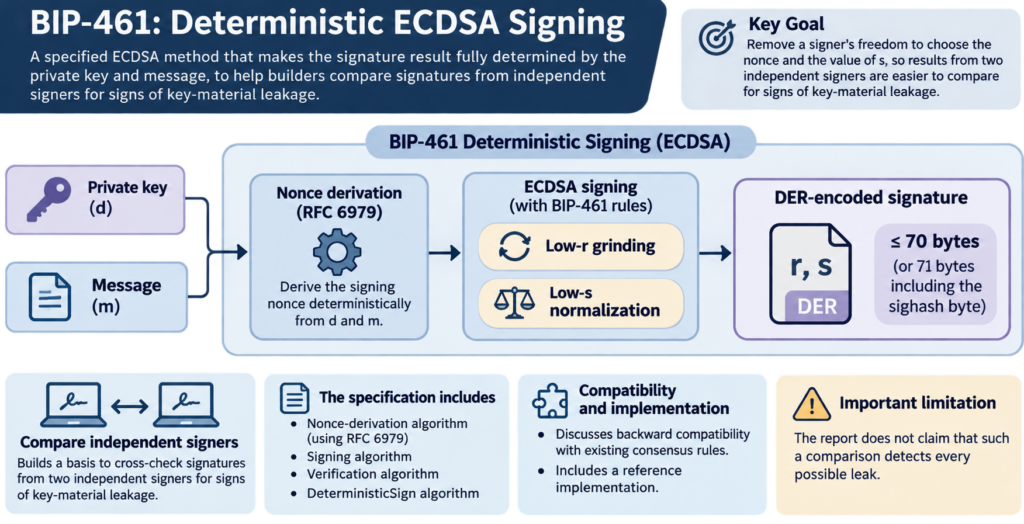
For builders comparing signatures produced by independent signers, BIP-461 specifies an ECDSA signing method in which the private key and message determine the result. The specification was described in the original report dated November 18, 2026.
The method derives the signing nonce—a value used when creating a signature—using RFC 6979. It then applies low-r grinding and low-s normalization. Under the specified method, a DER-encoded signature is at most 70 bytes, or 71 bytes with the sighash byte included.
By removing a signer’s freedom to choose the nonce and the value of s, the method is intended to make it easier to compare results from two independent signers for signs of key-material leakage. The specification also presents nonce-derivation, signing, verification and DeterministicSign algorithms, and discusses backward compatibility with existing consensus rules and a reference implementation. The report does not claim that such a comparison detects every possible leak.