Managing a mining fleet means keeping each machine pointed at the intended mining pool. In reporting published November 17, 2026, Luxor Technology said an attacker had used its Commander fleet-management tool to redirect machines belonging to just over a dozen client accounts to a different pool for a limited period. That sent the value of their computing work elsewhere, according to Luxor.
Luxor said its internal monitoring detected the unauthorized change. It patched Commander within two hours and began restoring the affected machines’ settings. The company said the issue was confined to Commander: Luxor Pool and LuxOS were not affected, and no data was leaked or taken from its systems. Luxor said it would pay affected clients in full for the redirected hashrate—the computing power used to mine Bitcoin—as though their machines had mined normally.
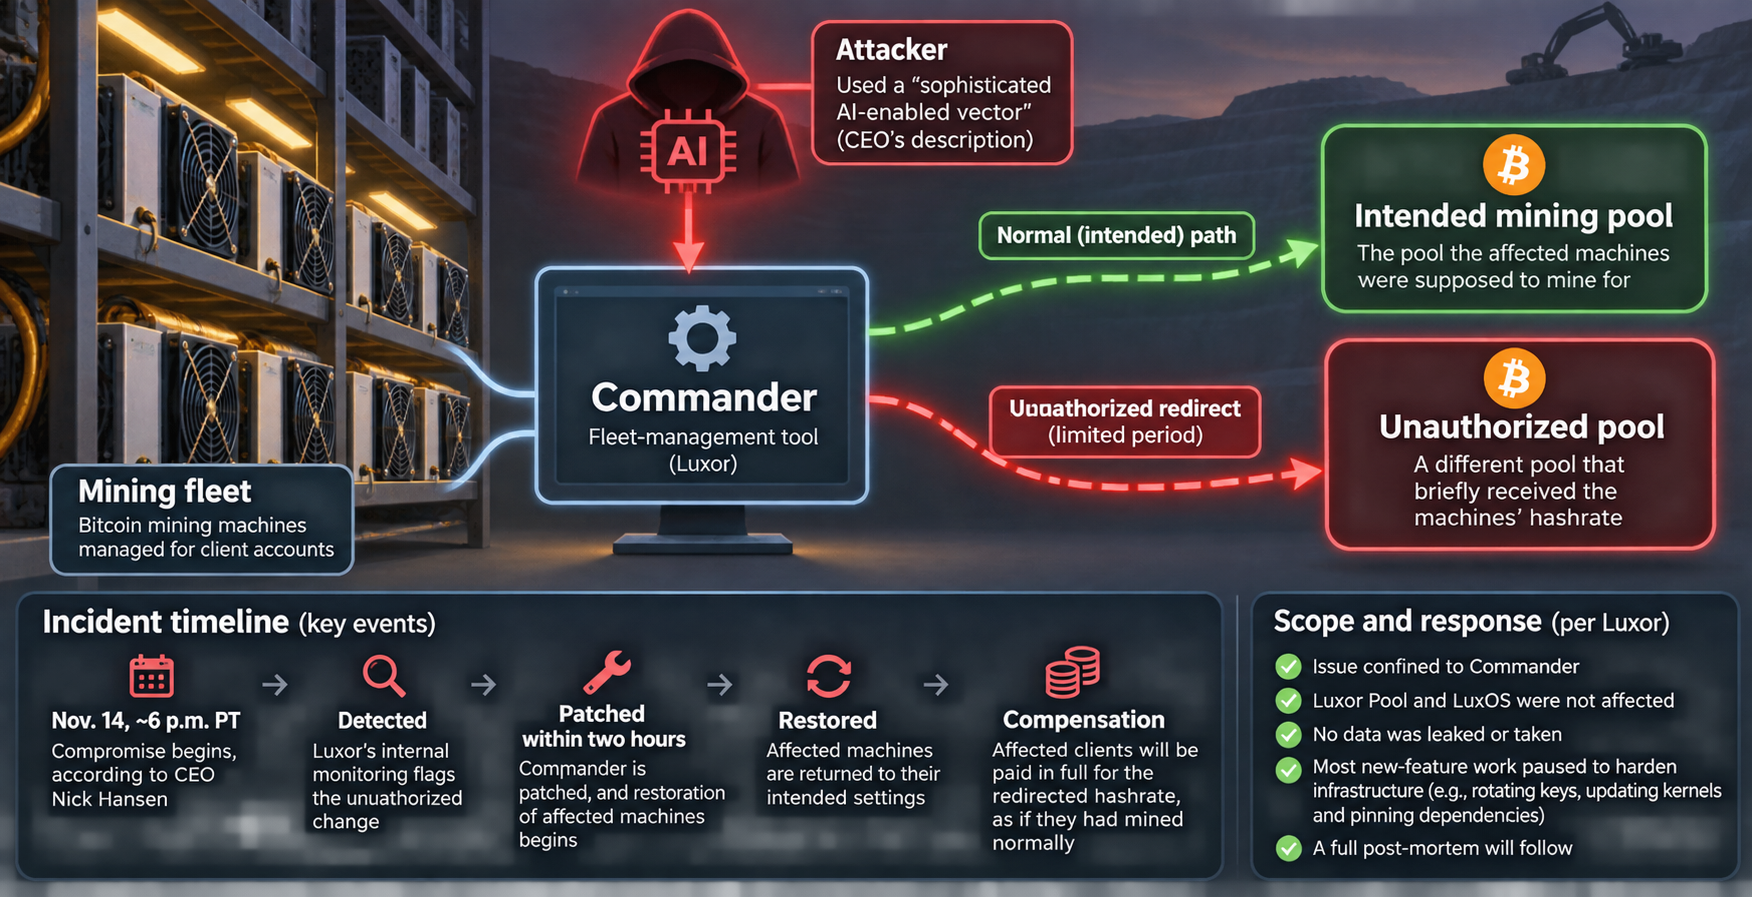
CEO Nick Hansen said the compromise began around 6 p.m. Pacific time on November 14. He described the attack as using a “sophisticated AI-enabled vector” but did not explain how it worked. The AI characterization is therefore Hansen’s, not a disclosed technical finding.
Hansen said Luxor had paused most new-feature work to strengthen its infrastructure, including rotating keys, updating kernels and pinning dependencies. Luxor said a full post-mortem would follow; none was included in the original report.