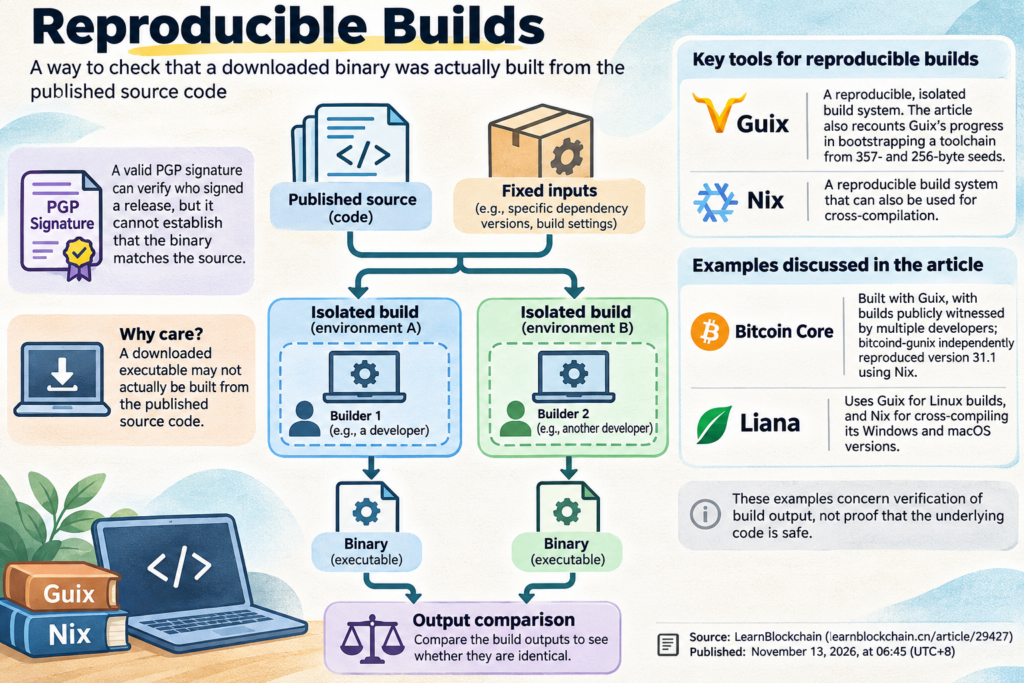
Before running a downloaded program, a builder may want to know whether its binary—the executable file—was actually built from the published source code. A valid PGP signature can help verify who signed a release, but it cannot establish that the binary matches that source.
In an article published on November 13, 2026, at 06:45 (UTC+8), LearnBlockchain explains how reproducible builds address that gap: separate builders use fixed inputs and isolated build environments to produce output they can compare. The article discusses Guix and Nix as tools for this process and recounts Guix’s progress in bootstrapping a toolchain from 357- and 256-byte seeds.
The article describes Bitcoin Core’s Guix builds as publicly witnessed by multiple developers, and says bitcoind-gunix independently reproduced version 31.1 using Nix. It also reports that Liana uses Guix for Linux builds and Nix for cross-compiling its Windows and macOS versions.
These examples concern verification of build output, not proof that the underlying code is safe. The original article also covers signature and hash checks and steps for reproducing Bitcoin Core and Liana builds; its commands and prerequisites are not included in the supplied account, so they are not reproduced here.
Source: learnblockchain.cn (originally published 2026-11-13 06:45 UTC+8)